Technologie
IA et Santé : Révolution Digitale pour les Entreprises Marocaines
Et si l'intelligence artificielle pouvait transformer votre approche du marketing digital et de la transformation digitale au Maroc ? Une récente étude sur...
Découvrez nos derniers articles sur le développement web, le design et les technologies digitales qui façonnent l'avenir
Et si l'intelligence artificielle pouvait transformer votre approche du marketing digital et de la transformation digitale au Maroc ? Une récente étude sur...
Les AirPods Pro 3 sont affichés à 209 € sur Amazon depuis le 15 octobre, contre environ 249 € chez Boulanger, la Fnac et Darty. Cette guerre des prix...
The current narrative around artificial intelligence in the workplace is largely driven by Silicon Valley. But treating the tech sector as an island misses the actual trends in technology adoption–tech is just the first industry in line. As generative AI and automation tools mature, the shifts...
Mise à jour HomePod 27.2 : ce que les entreprises marocaines peuvent en apprendre Apple vient de réserver une surprise aux propriétaires d'anciens HomePod...
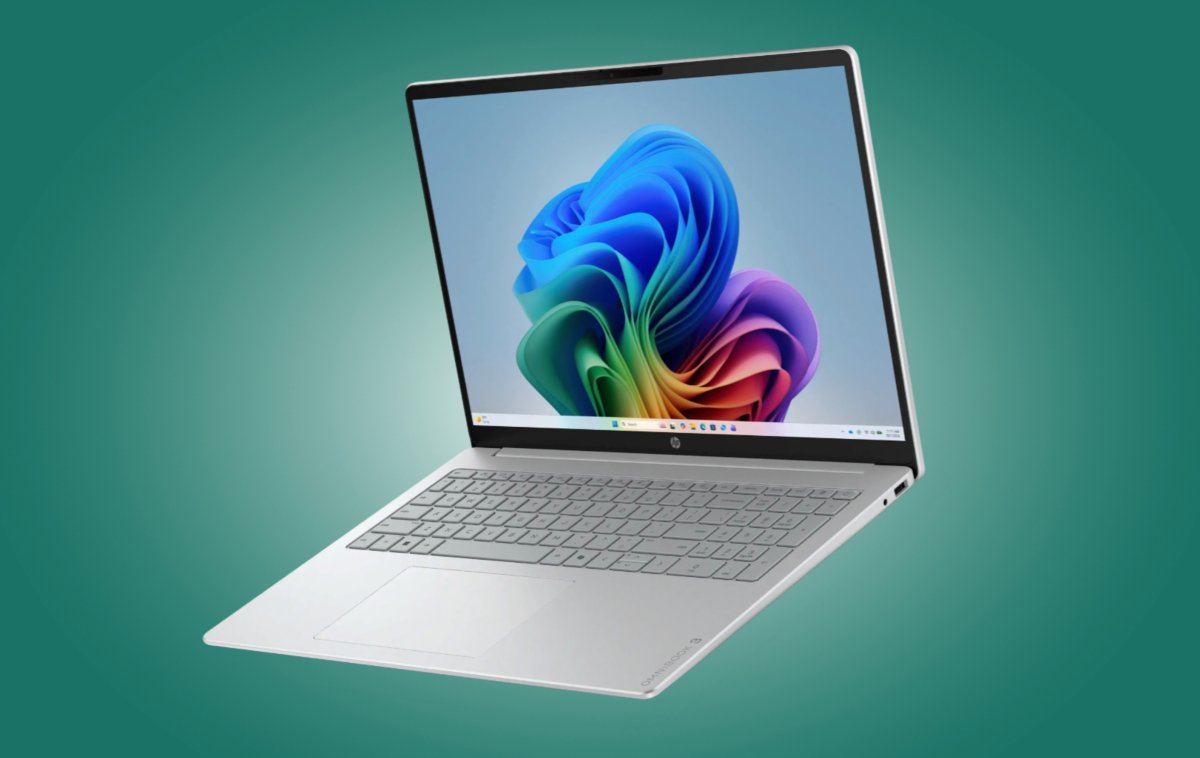
Le HP OmniBook 3 avec Snapdragon C promet jusqu'à 20 heures d'autonomie à petit prix. Découvrez comment cette innovation peut transformer votre stratégie...

Face aux coupures d'électricité fréquentes au Maroc, les solutions d'alimentation autonome séduisent particuliers et entreprises. Mais au-delà du produit,...

Andrew Haverdink, a tall grad student in a rain bib and rubber boots, wrenched a double-handed drill from the frozen soil that underlies much of Alaska’s Denali National Park and then unclipped the hollow barrel from the end of the bit. He knelt in front of a blue tarp, lined the barrel up...

In the fall of 2025, Jeff Dodge set up a six-foot folding table in the cafeteria of Cane Bay High School in Summerville, South Carolina, to conduct a taste test. When the first rush of about 150 hungry students hit, he was waiting with slow cookers filled with steaming marinara sauce and...

L'essor fulgurant de l'IA transforme l'économie mondiale et redéfinit les règles du jeu digital. Découvrez comment les entreprises marocaines peuvent tirer...
Et si une simple console de jeu pouvait exécuter des modèles d'intelligence artificielle à plus de 100 tokens par seconde ? C'est le défi relevé par PS5LM...
Il y a quelques jours, durant la conférence Hexacon à Paris, un chercheur nommé Quentin Kaiser a rendu publique une faille de sécurité qui traîne depuis au moins 2010 dans la fonction WPS de Broadcom. Je dis "qui traine" au présent parce qu'elle n'est toujours pas patchée évidemment....
Octave Klaba a averti sur une compromission de la CLI d'OVHcloud. Il précise sur X : "La version CLI de 14h47 a été compromise par un hacker. Nous l'avons détecté et bloqué à 16h21. Merci au client qui nous a remonté le souci. La version compromise est v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0. La...